Trust, Security & Compliance
AmplifAI provides enterprise-grade security, privacy, and compliance practices designed to protect your data at every level.
Enterprise Trust & Security
A security-first foundation for enterprise AI
Trust is foundational to how AmplifAI is built and operated. Our platform is designed to meet enterprise security, privacy, and compliance requirements across infrastructure, data, and AI operations.
Secure infrastructure
AmplifAI is built on Microsoft Azure, also working with AWS, GCP, and can be deployed inside client cloud infrastructure with enterprise-grade security controls including Sentinel and Defender, with data encrypted using 256-bit AES both in transit and at rest.
Privacy-first data handling
Customer data is processed strictly for defined purposes. We don't store call recordings long-term, we analyze, transcribe, and link back to your system of record, keeping sensitive data off our servers.
Governed AI operations
AI models operate within walled-off environments using internally-hosted LLMs. Your data never touches public APIs and is never used to train models for other customers.
Secure Foundation
Built on a secure foundation
AmplifAI is Trusted by Fortune 500 enterprises in healthcare, finance, and insurance.
Complete data isolation
Each client operates in a logically separated environment with no commingling of data between customers. Your data remains exclusively yours.
Data sovereignty controls
Region-lock your data to specific geographic locations. EU data stays in the EU, Australian data stays in Australia; your data never crosses borders without authorization.
Deployment flexibility
Cloud-first with options for on-premise or private cloud deployments. Run AmplifAI within your own FedRAMP-authorized Azure environment or secure banking infrastructure.
Compliance & Certifications
Certified for the standards that matter
AmplifAI maintains critical industry certifications, meeting the rigorous standards required by highly regulated industries including healthcare and finance.
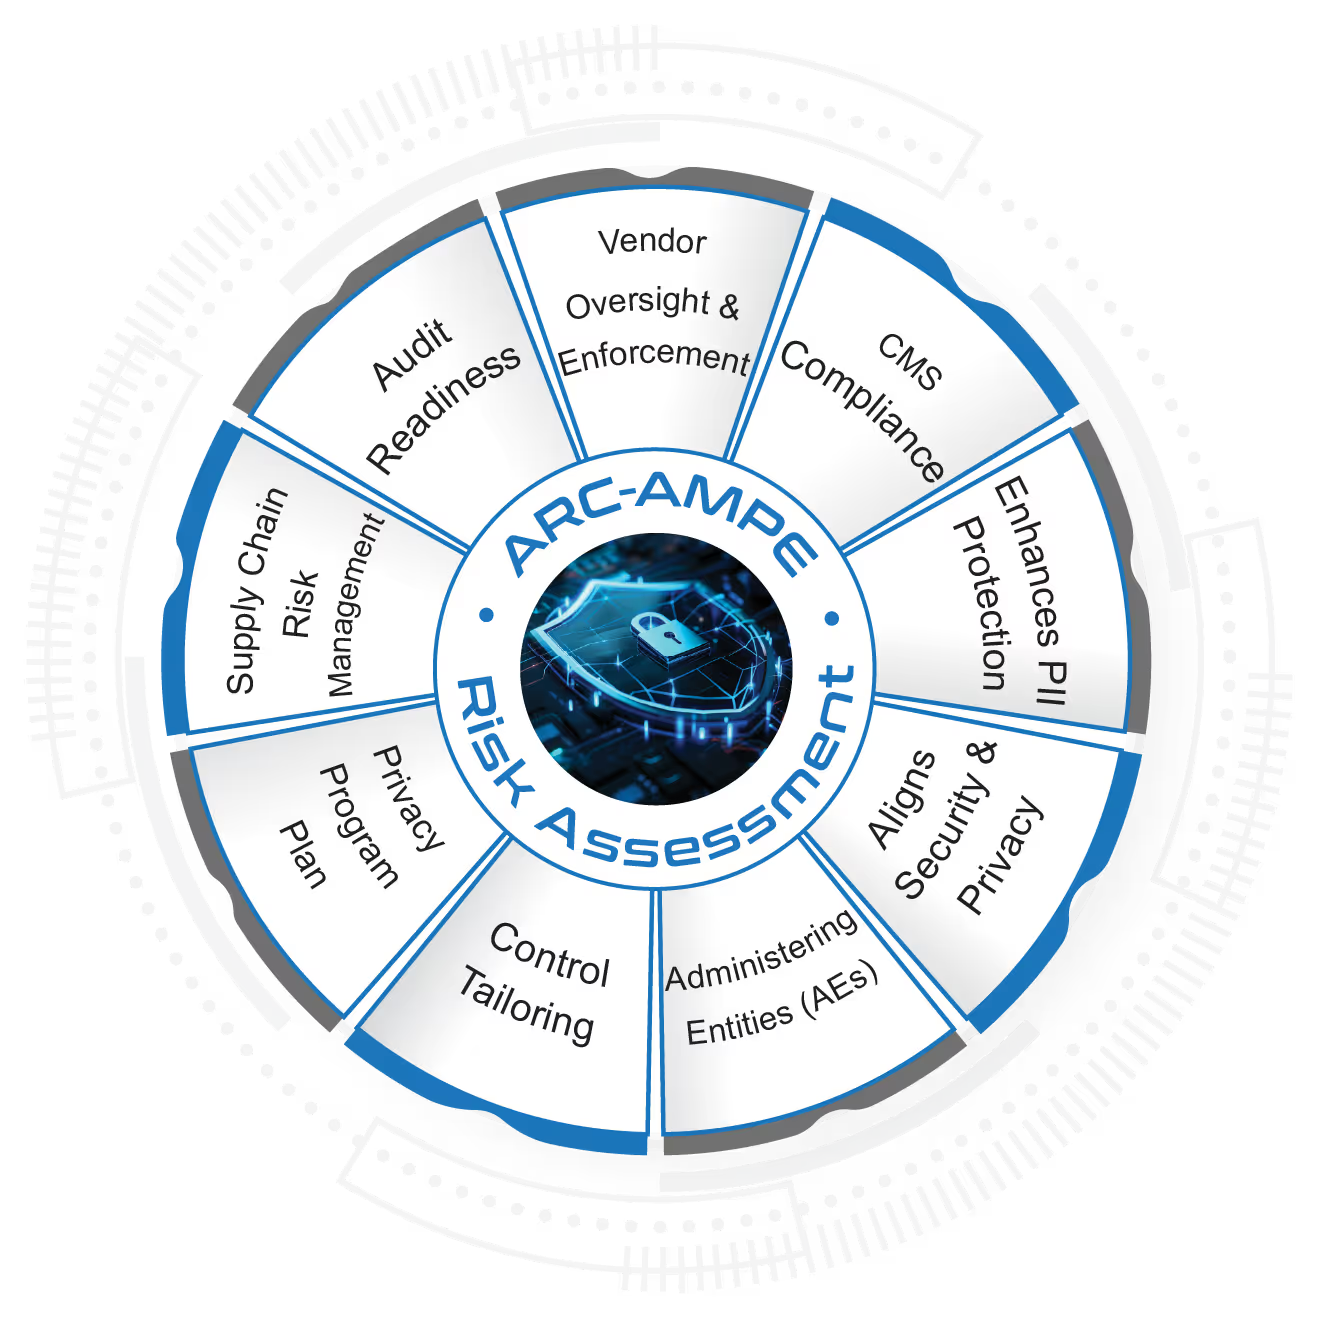
ARC-AMPE Risk Assessment
Enhanced protection of Personally Identifiable Information (PII)
With the increasing sensitivity around personal data, ARC-AMPE more deeply integrates privacy controls to ensure stronger protection.
Stronger privacy and security alignment
The framework improves collaboration across privacy, security, and IT domains by embedding privacy earlier in the control lifecycle.
Better alignment with federal standards
ARC-AMPE incorporates elements from updated frameworks like NIST 800-53 Rev5, making it more consistent with broader federal expectations.
Source: SP 800-53 Rev. 5, Security and Privacy Controls for Information Systems and Organizations | CSRC
Responsible AI
Setting the standard for responsible AI
Responsible AI is core to how AmplifAI designs and operates intelligent systems, with accountability, transparency, and human oversight built in.
Isolated model architecture
We use open-source LLMs like LLaMA hosted internally within our secure cloud. Your data never leaves our environment to reach public APIs like ChatGPT.
Your data trains only your models
Client data is never used to train a master model that benefits other customers. Models are tuned specifically and exclusively for your organization.
Human-in-the-loop by design
Our AI powers coaching and QA for your teams: it's employee-facing, not customer-facing. This eliminates the risk of AI hallucinations reaching your consumers.
PII/PHI protection built-in
Automatic redaction of sensitive data including SSNs, credit card numbers, birth dates, and health information before AI processing, whether you redact pre-ingestion or we handle it post-ingestion.
Sovereign Data Architecture
Trust and Compliance FAQ's
AmplifAI enforces sovereign data architecture, client-segregated environments, and opt-out training guarantees across every deployment.
Sovereign AI Architecture: Where does the conversation data AmplifAI collects go?
AmplifAI is deployed in a secure, client-segregated cloud architecture built on Microsoft Azure infrastructure. Conversation data (calls, transcripts, QA artifacts, survey data, etc.) flows through a structured ingestion and processing pipeline and is stored in logically segregated client environments.
From the documented architecture:
- Data is ingested via API, SFTP, email, SQL/Snowflake connections
- Processing occurs in dedicated SQL/Document DB environments
- Storage includes Azure Blob and Cosmos DB with geo-replication options
- Architecture is resilient, load-balanced, and enterprise-grade
Additionally, AmplifAI enforces:
- Data privacy with segregated data per customer
- Secure transfer mechanisms (API, SFTP, secure storage)
In Practice:
- Conversation data is stored in the client’s dedicated cloud environment.
- Data is logically segregated by client.
- Data is not co-mingled across customers.
- Secure ingestion, processing, and storage follow enterprise cloud standards.
If required, regional deployment options (see below) can further restrict data residency.
Localized Cloud Footprints: Does AmplifAI run locally or in-region?
Yes, AmplifAI supports regional deployment within Azure environments, and we work across AWS and GCP as well. AmplifAI's platform architecture is cloud-based and designed with geo-replication and distributed infrastructure support.
Deployment Options:
- In-region Azure deployment (e.g., North America, Europe, APAC depending on client requirements)
- Geo-replication configurations for resilience and compliance
- Secure enterprise ingestion and processing layers
- AWS
- GCP
What This Means:
- AI models operate within the provisioned regional cloud instance.
- Data residency requirements (e.g., EU-only processing) can be supported.
- No data must leave the designated cloud region unless explicitly configured.
If strict sovereign requirements exist (e.g., public sector or financial services), deployment architecture can be aligned accordingly during implementation.
Opt-Out Training Guarantees: Is my company’s data used to train AmplifAI's model?
AmplifAI operates under a segregated customer data model.
Key points:
- Customer data is isolated per tenant.
- Models are tuned for the customer’s environment.
- Data is used to improve that customer’s AI performance within their instance.
- Customer data is not pooled across clients to train shared global models.
Additionally, autoQA calibration is customer-specific and relies on that customer’s evaluation forms and call samples.
AmplifAI Ensures:
- Your data is used to power your AI experience.
- It is not used to train models for other customers.
- No cross-client data sharing or training occurs.
- Model tuning and calibration are customer-specific.
Enterprise-Ready Principles
Enterprise-ready by design
Designed to support enterprise security, privacy, and operational resilience at scale.
Enterprise-grade infrastructure
Built on Microsoft Azure with native security features, 256-bit AES encryption, and the flexibility to deploy on-premise or in private cloud environments for maximum control.
Privacy by design
We don't need to own or store your sensitive recordings. Data is analyzed and linked back to your system of record, with configurable retention from 12 months to custom deletion protocols.
Shared security commitment
SSO integration with Okta and Azure AD, role-based access control ensuring agents see only their data, and strict hierarchy-based permissions across your organization.
Built for Trust
Enterprise AI, built for trust
AmplifAI enables organizations to deploy AI with confidence by combining advanced intelligence with security, privacy, and compliance at the core.